Posts

Showing posts with the label student

More mitigations

Image
 So like I said we are going over mitigations and I grabbed a couple slides and while this is not everything, I grabbed ones that helped to spark a thought process and understand how mitigation can be performed. Now we started with SMB Relay because we were told its one of the most exploited vulnerabilities. Really until this slide I was thinking "if it's such a known vulnerability why is it still being used?" And seeing this slide with the pros and cons made me realize certain things need to be used and our job as security professionals can't be just to shut down everything that can be exploited but rather make things as safe as possible so that our companies can still be as productive as possible while being as safe as possible. Now I always thought I knew strong passwords but in taking this course I found out just how easy password cracking is. So, 14 or more characters and make it complex.  Capital, Lowercase, Numbers, Special Characters, stay away from common wor...
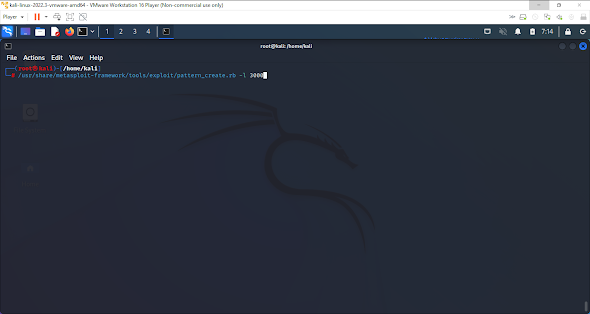
Offset

Image
What I am doing here is finding the offset. Again this is all enumeration for the end attack. The more information we have the easier it is to overload this machine.  Remember to run vulnserver and immunity debugger as Admin and attach them. And here we are using the number of 3000, why is that. Well if you remember in the last blog the tipping point was 2900, so now we are ensuring enough characters will be used.  We get this printout and we are going to copy it to put in our script. A few things to note. We no longer need the time so we erased that. We set our "offset" to what we just copied and pasted and we are no longer using a while loop.  I took this picture to make a point. Make sure you copy the characters exactly. I had a single space after the last "9" and it messed up my whole script. So we removed the space, ran the program and as you can see we achieved overloading it and its paused.  Now in a very messy was I have highlighted the important part here. ...

Spiking and Fuzzing

Image
 Here we started getting an introduction to some new tools. Using vulnserver, and immunity debugger. We did this as an introduction to exploit development. So the first thing you need to do is go out and download both vulnserver and immunity debugger. Now that you've done that run both vulnserver and immunity debugger as administrator  Then attach vulnserver to immunity debugger and press play. Make sure in the bottom right it says "Running" Here we use "nc" and "-nv" with the ip address of the target server with a port of 9999 to gain access and then we used 'HELP" to print out all the valid commands. Here we use the command "generic_send_tcp" with our ip address and por 9999 and trun.spk. Now to be honest I dont 100% remember what the following2 zeros are for as this was a few weeks ago and like many people I dont remember every single detail (hence the screenshots and this blog) And here you see its paused again because we have ju...

BlackPearl Exploit

Image
 Now this exploit for my rig was a little hard just because I do not have the most RAM and it required slightly more than the others. So I took less screenshots  This again is the same step as the others. Figuring out what ports were available  Here we are using "ffuf" again Now I believe this is the first time we used "dnsrecon" And here we add the dns to our machine so we can perform the attack Follow me at  LinkedIn  or  Twitter

The Dev Exploit

Image
This is the Dev machine through  TCM's  Practical Ethical Hacking course. Here we did the same thing as the last box "dhclient" and "ip a"  Here we run "nmap" to find open ports. This is the fourth or fifth exploit and what I have realized is the first several steps, rather it's on a windows or Linux machine, is the same. Here I showed all the ports because some of the important ports were a little out of site on the previous slide Here we are obtaining some vital information. We were able to see the php page and get some good information.  Using "ffuf" again to gain some enumeration. Here we used "searchsploit" for the first time.  Now following this we used the information gathered to gain privilege escalation and captured the flag. Follow me on  LinkedIn  or  Twitter

The Academy Exploit

Image
 This is the Academy VMware exploit. I was asked not to post the whole thing so I have most of it on here. This is me getting access to the box First you run "dhclient" then "ip a" to get the ip address of the box you are going to attack  Here we run "nmap" to find out what ports are open, what can we exploit? Here we use "ftp" to connect and see an interesting "note.txt" file Here we "cat" the "note.txt" file. If you notice it gives us a lot of valuable info Here we use "dirb" to directory bust the target Here is the first time I used "ffuf"  Here listened and were able to obtain root access and capture the flag Follow me or reach out at  LinkedIn  or  Twitter

Dictionaries

Image
 This is my notes on dictionaries. I found this a fairly straight forward code.  Feel free to reach out on  LinkedIn  or  Twitter  

Functions in Python

Image
 Here are my notes from the functions lesson of the PEH. I think this was a fairly easy lesson to follow along with. My biggest take away I think is the importance of the indentation. As well as the fact that you can have single or multiple parameters. And as a reminder the '#' on the right-hand side of the code are my notes for later. I have always like keeping shorthand reminders that call back things rather than long drawn-out notes. But if you need any clarification please comment or message me on my social medias and I will try and elaborate.  Remember feel free to contact me on  LinkedIn  or  Twitter

Boolean Expressions

Image
 This lesson was short and sweet and easy to understand. So, a Boolean expression is just an expression of true and false. Which my understanding is that it comes in handy later on when you call functions like, if such and such is true then do blah. Please find me on  LinkedIn  or  Twitter

Math in Python

Image
Today was pretty fun. It was a simple lesson but one I think will be handy. I am a huge math geek. My 3 year old and I randomly add the numbers we see on the street and he is getting to the point he can do his multplication tables up to 10 already. So learning that python can do math by scripting it makes sense but I can also see how that might be handy in the future when I am writing more advanced scripts for vulnerabilities in a system. As I am sure I have said pentesting isnt where I want to stop. I want to go full red team and overall I want to be good at as much in cyber as possible. I mean the goal is to do as much good with this knowledge as possible so learning scripting on all angles would make me more effective but anyways, we did some simple scripting for math and it sounded like we will get to the more advanced in a later lesson.  Check it out and if you know of some simple scripts I can add to my math knowledge let me know I would love to give it a try. Feel free to re...